
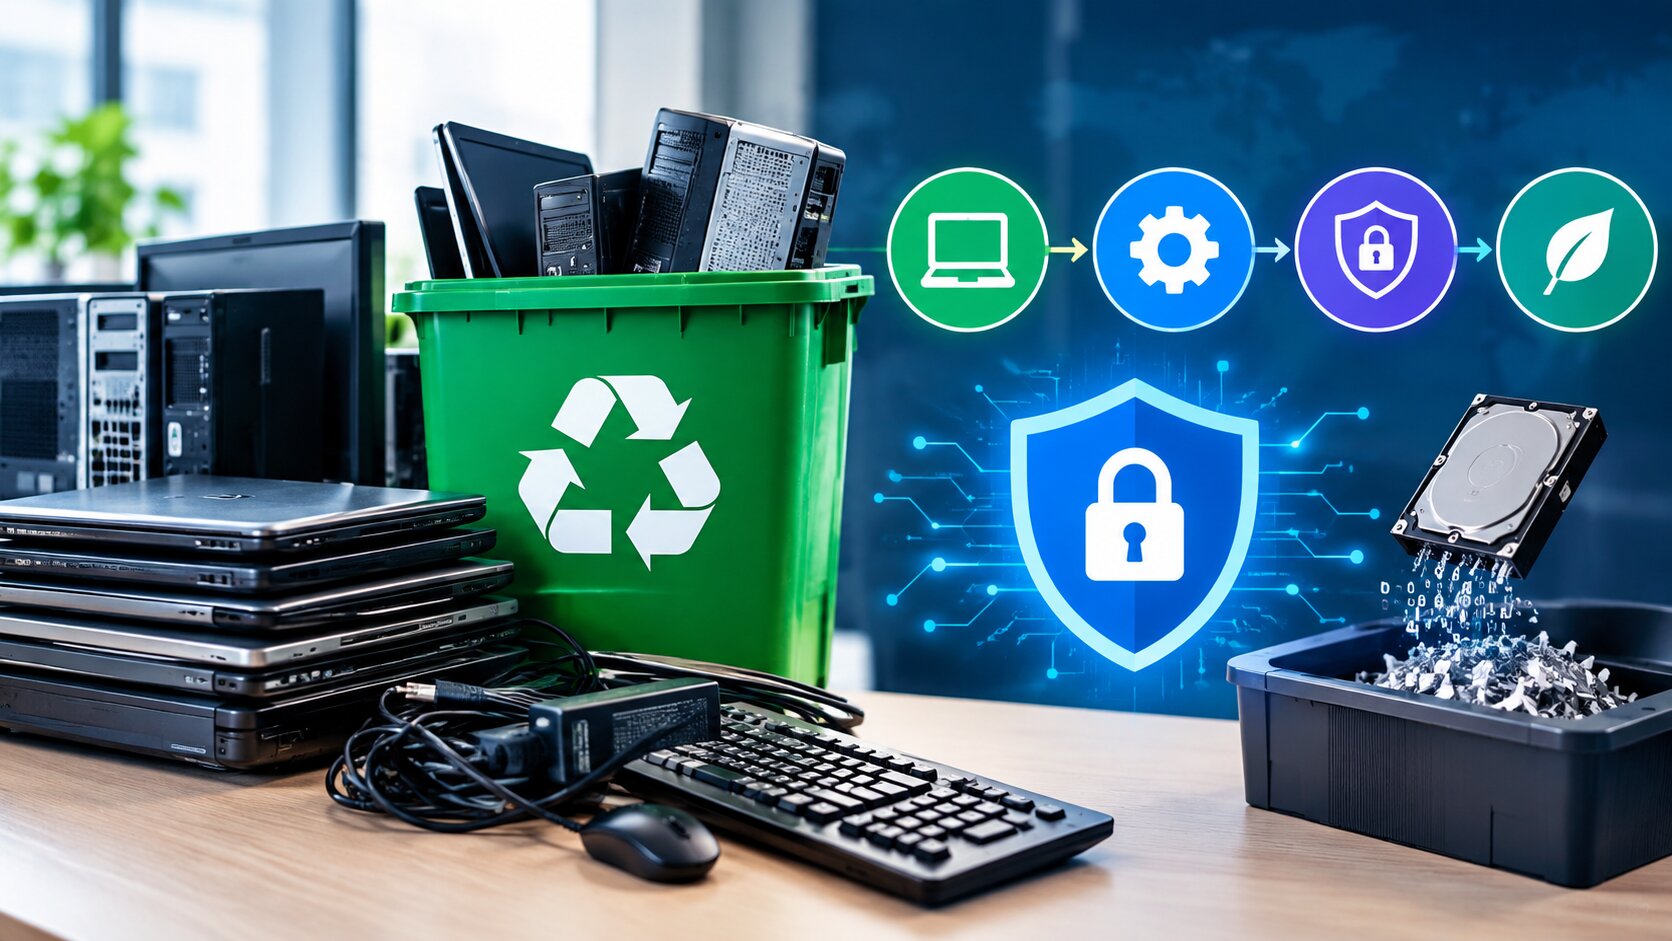
A retired server doesn’t stop being a security risk just because it’s unplugged. Every drive it carried still holds data, and that data doesn’t disappear on its own. ITAD exists to handle exactly that problem. Here’s what it covers, why it matters more than most companies realize, and how to build a program that actually protects you.
Key Takeaways
- ITAD (IT Asset Disposition) is the process of securely retiring, wiping, and disposing of outdated IT equipment.
- It includes data destruction, asset tracking, and compliant recycling or resale.
- Improper disposal creates real data breach risk, since drives often still hold recoverable data.
- Chain-of-custody documentation protects your organization during audits and breach investigations.
- ITAD works alongside broader practices like data center migration planning and secure data erasure.
What Does ITAD Stand For?
ITAD stands for IT Asset Disposition, the structured process of securely retiring, wiping, and disposing of outdated or unused IT equipment. This includes servers, laptops, hard drives, networking gear, and any other device that once held company data. Data breach investigations have repeatedly traced sensitive information leaks back to improperly disposed hardware, which shows exactly why ITAD deserves formal attention rather than ad-hoc handling. Related concepts include data sanitization, chain of custody, e-waste recycling, and asset tracking.
In simple terms, ITAD answers a question most companies don’t think about until it’s too late: what actually happens to a device, and the data on it, after it stops being useful?
What ITAD Actually Covers
A complete ITAD program spans several distinct steps, not just physically removing old equipment from a rack.
- Asset inventory and tracking — Documenting every device slated for retirement, including serial numbers and data classification.
- Data destruction or sanitization — Securely wiping or physically destroying storage media so data cannot be recovered.
- Chain-of-custody documentation — Tracking each asset’s location and handling from removal through final disposition, creating an audit trail.
- Compliant recycling or resale — Disposing of hardware through certified e-waste recyclers, or reselling functional equipment through proper channels.
- Certificate of destruction — Obtaining formal documentation proving data destruction occurred, which matters significantly for compliance audits.
Why Improper ITAD Creates Real Risk
Recoverable data on “deleted” drives
Simply deleting files or formatting a drive doesn’t actually erase the underlying data. Specialized recovery tools can often retrieve information from drives that weren’t properly wiped, which is exactly how sensitive data ends up in the wrong hands.
Compliance and legal exposure
Many regulations, including data privacy laws, hold organizations accountable for what happens to data even after a device leaves company control. Improper disposal can trigger compliance violations and legal liability.
Reputational damage
A publicized data breach traced back to improperly disposed hardware damages trust in ways that are hard to repair, regardless of how the rest of a company’s security program performs.
ITAD Methods: Comparison
| Method | Data Security Level | Environmental Impact | Best For |
|---|---|---|---|
| Physical destruction (shredding) | Highest | Requires proper recycling to avoid waste | Highly sensitive data, end-of-life drives |
| Certified data wiping | High | Enables hardware reuse/resale | Functional equipment being resold or donated |
| Degaussing | High (for magnetic media) | Requires proper recycling | Hard drives, magnetic tape |
| Simple deletion/formatting | Low, not recommended | N/A | Not suitable for sensitive data disposal |
Why ITAD Matters for Security Teams
“Companies spend heavily on securing active systems, then hand off retired hardware to whoever’s cheapest without a second thought. That gap is exactly where a lot of preventable breaches originate.” — Thomas Reyes, IT Security and Compliance Director, Enterprise Asset Management Group, 2025.
Retired hardware often gets deprioritized simply because it’s no longer in active use, but the data risk doesn’t disappear with it. This is particularly relevant during larger transitions like a data center migration, when large volumes of equipment get retired at once, or during routine data cleaning and maintenance cycles that identify aging hardware for replacement.
How to Build an ITAD Program
- Create a formal disposition policy — Document exactly how retired equipment should be handled, including who’s responsible at each step.
- Classify data sensitivity before disposal — Determine the appropriate destruction method based on what data the device held, since not every device needs the same level of destruction.
- Choose a certified ITAD vendor — Work with vendors holding recognized data destruction and environmental certifications, rather than the lowest-cost option without verification.
- Maintain chain-of-custody records — Track every asset from removal through final disposition, and require documentation at each handoff point.
- Obtain certificates of destruction — Collect and retain formal proof of data destruction for every disposed asset, supporting future audits or investigations.
Frequently Asked Questions
What does ITAD stand for?
ITAD stands for IT Asset Disposition, the structured process of securely retiring, wiping, and disposing of outdated IT equipment.
Is deleting files enough to protect data on old devices?
No. Deleting files or formatting a drive typically leaves underlying data recoverable with specialized tools, which is why proper data sanitization or physical destruction matters for sensitive information.
Can retired IT equipment be resold safely?
Yes, when data has been properly wiped using certified sanitization methods and documented with a certificate of destruction, functional equipment can often be safely resold or donated.
Who should handle ITAD for a company?
Many organizations use certified third-party ITAD vendors specializing in secure data destruction and compliant recycling, rather than handling disposal internally without proper equipment and certifications.
Does ITAD apply to cloud-based companies without physical servers?
Yes, to a lesser degree. Even cloud-first companies typically have laptops, mobile devices, and office equipment that require proper disposition when retired.
Conclusion
ITAD closes a security gap that’s easy to overlook: what happens to data-bearing equipment after it stops being useful. Without a formal process covering tracking, destruction, and documentation, retired hardware quietly becomes one of the more preventable sources of data exposure. Building a proper ITAD program, backed by certified vendors and clear chain-of-custody records, turns that risk into a manageable, auditable process instead of an afterthought.
For related reading, see our guides on data center migration planning, secure data erasure, and data center cleaning standards.