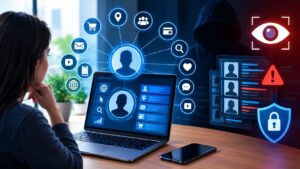

Identity sprawl is the uncontrolled growth of user, service and application accounts across an organization systems, clouds and apps, often managed in different places with different rules. As employees, contractors, apps, bots and cloud workloads each get their own accounts and credentials, nobody has a full picture of who and what has access. That gap creates security, compliance and cost problems.
Key takeaways
- Identity sprawl covers human accounts and non-human identities such as service accounts, API keys, tokens and bots.
- It grows through cloud adoption, SaaS, mergers, shadow IT and weak offboarding.
- The main risks are orphaned accounts, excess privileges, reused credentials and failed audits.
- You reduce it by discovering every identity, centralizing authentication, enforcing least privilege and automating the account lifecycle.
- Regular access reviews keep the problem from coming back.
What is identity sprawl?
Identity sprawl is the situation where an organization has far more identities and accounts than it can track and control. A single employee may have separate logins for email, a ticket system, several SaaS apps and cloud consoles. Add contractors, test accounts, service accounts, API keys and machine identities, and the total can grow faster than the security team can review. Non-human identities often outnumber human users in cloud-heavy environments, which makes them a growing blind spot.
What causes identity sprawl?
Identity sprawl is caused by growth without a central way to create, track and remove access. Common causes include:
- SaaS and cloud adoption. Each new app or cloud account brings its own user directory. This is closely related to cloud sprawl.
- Shadow IT. Teams sign up for tools without telling IT, so accounts exist outside any process.
- Mergers and acquisitions. Different directories and systems get stacked on top of each other.
- Poor offboarding. When people leave or change roles, old accounts and permissions stay behind.
- Service accounts and API keys. Developers create them for convenience and rarely rotate or retire them.
- Many authentication systems. On-premises directories, cloud identity providers and local app accounts coexist.
What are the risks of identity sprawl?
The main risk is that attackers need only one forgotten or weak identity to get in. Key risks are:
- Orphaned accounts. Accounts of former staff stay active and can be abused.
- Excessive privileges. Permissions pile up over time, so users hold far more access than their role needs.
- Credential reuse and weak passwords. More accounts mean more reused passwords, which helps credential stuffing and phishing. See how to spot these attacks in our guide to phishing emails.
- Unmanaged machine identities. Long-lived keys and tokens in code or configuration are easy targets.
- Compliance gaps. Auditors expect you to prove who has access to what, and sprawl makes that hard.
- Higher cost and effort. Unused licenses, duplicate accounts and manual access requests waste money and time.
These risks appear in broader threat lists such as our overview of the top cybersecurity threats in 2026.
What are the signs of identity sprawl?
Warning signs include accounts nobody can explain, slow offboarding and inconsistent access rules. Look for:
- Active accounts for people who have left.
- Several accounts for the same person across systems.
- Service accounts with no owner or no expiry.
- Apps that use their own local logins instead of single sign-on.
- Access reviews that take weeks or are skipped.
- Audit findings about excessive or undocumented access.
How do you reduce identity sprawl?
To reduce identity sprawl, discover every identity, consolidate authentication, enforce least privilege, review access and automate the lifecycle. The flow below shows the order.
- Discover and inventory. Pull accounts from directories, cloud platforms, SaaS apps, code repositories and secret stores. Include service accounts, API keys and bots, and assign an owner to each one.
- Consolidate authentication. Use a central identity provider with single sign-on and federation, and move apps off local accounts where you can.
- Enforce strong authentication. Require multi-factor authentication, especially for admins, as described in our guide to two-factor authentication.
- Apply least privilege. Use role-based access control, remove standing admin rights and give temporary privileged access with approval.
- Run regular access reviews. Have managers and system owners confirm who needs what, and remove the rest.
- Automate joiner, mover and leaver steps. Connect HR systems to identity tools so accounts are created, changed and removed on time.
- Manage secrets and machine identities. Store keys in a vault, rotate them and set expiry dates.
- Detect shadow IT. Use discovery tools and expense or login data to find unmanaged apps.
- Document policy. Define who can create identities and how long data is kept, using templates such as our data retention policy.
Smaller organizations without a full security team can get guidance from a virtual CISO.
Which tools help with identity sprawl?
Several tool categories address identity sprawl. Use the category that matches your gap:
| Tool category | What it does |
|---|---|
| Identity provider and SSO | Central sign-in, MFA and app federation |
| Identity governance and administration (IGA) | Access requests, reviews and lifecycle automation |
| Privileged access management (PAM) | Vaulting, session control and just-in-time admin access |
| Cloud infrastructure entitlement management (CIEM) | Finds excess permissions in cloud accounts |
| Secrets management | Stores and rotates keys, tokens and passwords |
| SaaS and shadow IT discovery | Finds unmanaged apps and accounts |
Features and names vary by vendor, so compare current options against your own environment before you buy.
Frequently asked questions
What is the difference between identity sprawl and cloud sprawl?
Cloud sprawl is the uncontrolled growth of cloud resources, such as servers, storage and subscriptions. Identity sprawl is the uncontrolled growth of accounts and credentials. They often grow together, because each new cloud service brings new identities.
What are non-human identities?
Non-human identities are accounts and credentials used by software rather than people, such as service accounts, API keys, tokens, certificates and bots. They need owners, limited permissions and rotation, like human accounts.
Does single sign-on solve identity sprawl?
SSO helps by centralizing sign-in, but it does not solve everything. Apps with local accounts, service accounts and over-privileged roles still need governance, reviews and lifecycle automation.
How often should access reviews run?
Many organizations review privileged access quarterly and normal access at least twice a year or annually. Follow your compliance requirements and risk level.
How do you find orphaned accounts?
Compare your account lists against your HR records and recent login activity. Accounts with no matching active person, or long inactivity, need review and removal.
Conclusion
Identity sprawl turns every forgotten account into a possible entry point. Start by finding every identity, consolidate sign-in, enforce least privilege and automate the account lifecycle, then keep checking with regular access reviews. Smaller, well-managed identity estates are easier to secure and audit.